Cybersecurity News

CMMC rule developments, prime contractor advisories, speaking engagements, and Cybersec Investments milestones — all in one place.

30+
Years DoD Experience
C3PAO
Accredited
SDVOSB
Veteran-Owned Business
SBA 8(a)
Small Business Certified
150+
Certificates Issued
2018
Founded
2026

July 17, 2026

Industry

Supplier Update: Elbit Systems of America on the CMMC Phase II Suspension

Elbit Systems of America has issued guidance to its suppliers following the Department of War’s suspension of the transition to CMMC Phase II. The letter emphasizes that existing cybersecurity requirements remain in effect and encourages organizations to continue implementing NIST SP 800-171, maintaining required documentation, and preparing for future CMMC Level 2 assessment requirements. 


The full letter is available below and provides additional details.


Read the letter by Elbit Systems of America: CMMC Phase II Suspension – Stay the Course
July 16, 2026

Company

Cybersec Investments Achieves ISO/IEC 170:2012 Accreditation as a C3PAO

Cybersec Investments has achieved ISO/IEC 17020:2012 Accreditation, further validating its commitment to quality, impartiality, and consistency as a CMMC Third-Party Assessment Organization (C3PAO). This milestone reflects Cybersec Investments’ continued dedication to maintaining rigorous assessment standards and delivering trusted CMMC assessment services within the cybersecurity compliance ecosystem.

As an accredited C3PAO, Cybersec Investments conducts CMMC assessments in accordance with the requirements of the CMMC ecosystem. This achievement reflects the organization’s focus on maintaining assessment integrity, operational consistency, and adherence to established quality standards.


The full press release is available below and provides additional details about this accreditation milestone.


Read the full press release: Cybersec Investments Achieves ISO/IEC 17020:2012 Accreditation

July 16, 2026

Industry

Statement from the CYBER AB about the suspension of CMMC Phase II

The CYBER AB responded to the Department of War’s decision to suspend CMMC Phase ll implementation requirements while a newly established CMMC Reform Task Force conducts a 60-day review of the program.

The CYBER AB states it was surprised and disappointed by the pause but remains confident that the CMMC program has demonstrated its value through measurable progress and the significant investments made by the DIB and CMMC ecosystem. It also stated that they will cooperate fully with the task force during the review.

To learn more about the statement released by the CYBER AB visit their website here: Statement on the Department of War’s Suspension of CMMC Phase II Requirements – CyberAB.

April 6, 2026

Industry

Lockheed Martin: Suppliers Must Maintain CMMC Status in SPRS and Exostar

In a supplier notice titled “Maintaining Cybersecurity Maturity Model Certification Status,” Lockheed Martin directed active suppliers to document their CMMC status in the DoD’s SPRS (at least a Final Level 1 self-assessment, and Final Level 2 where CUI is in scope), share that status with Lockheed Martin through the Cybersecurity Compliance Attestation (CCA) in Exostar Supplier Management, and keep it current with annual affirmations and assessments within required timeframes. Cybersec Investments performs accredited CMMC Level 2 assessments to help suppliers meet and maintain these requirements.

Read the Lockheed Martin release →

April 6, 2026

Industry

L3Harris Issues CMMC Requirement for Suppliers

L3Harris Technologies notified suppliers of CMMC requirements tied to DoD contracts. Suppliers handling CUI may be required to obtain CMMC Level 2 certification depending on contract requirements, with applicable suppliers asked to submit proof of certification by July 30, 2026. Cybersec Investments performs accredited CMMC Level 2 assessments to help suppliers meet these requirements.

February 12, 2026

Industry

GSA Blog: Cybersecurity Maturity Model Certification (CMMC)

The GSA Blog published a comprehensive guide on CMMC — covering the certification levels, requirements, and how to prepare. The CMMC sets cybersecurity standards for federal contractors. Cybersec Investments is available for a CMMC Level 2 Assessment.

January 9, 2026

Industry

Elbit Systems Urges Suppliers to Act on CMMC Level 2 Compliance

Elbit Systems of America informed suppliers that CMMC compliance is now mandatory. Level 2 certification from a C3PAO is required to continue receiving purchase orders and meet contractual flow-down requirements. Key actions: schedule a CMMC Level 2 assessment, update SPRS Cyber Reports, and pursue Level 2 certification to create new supply chain opportunities.

2025

December 1, 2025

Industry

Lockheed Martin: Suppliers Must Update CMMC Status in Exostar

Lockheed Martin required all active suppliers to submit their CMMC status via a Cybersecurity Compliance Attestation (CCA) in Exostar. Suppliers handling sensitive information with Moderate or Significant risk ratings should complete their CCRA questionnaire and conduct a CMMC readiness assessment. Cybersec Investments provides CMMC and SCF assessments to help suppliers build a clear compliance roadmap.

November 10, 2025

Industry

Department of Defense Finalizes CMMC Rule, Making Certification Mandatory for New Contracts

The DoD officially published the final rule for CMMC under 48 CFR, integrating it into federal acquisition regulations. CMMC certification is now a mandatory requirement for new contracts involving CUI, marking a significant milestone in federal cybersecurity standards. Cybersec Investments performs accredited CMMC Level 2 and SCF assessments in alignment with the new requirements.

November 5, 2025

Industry

Elbit Systems of America Issues Supplier Cybersecurity Notice

Elbit America released an important communication to its supplier community: if business requirements necessitate sharing CUI with a supplier, that supplier will be required to achieve CMMC Level 2 certification as defined in CFR § 170.17. Non-COTS technology suppliers must immediately conduct a Level 1 self-assessment and affirmation within the Supplier Performance Risk System (SPRS).

Elbit America supplier CMMC certification notice

October 28, 2025

Event

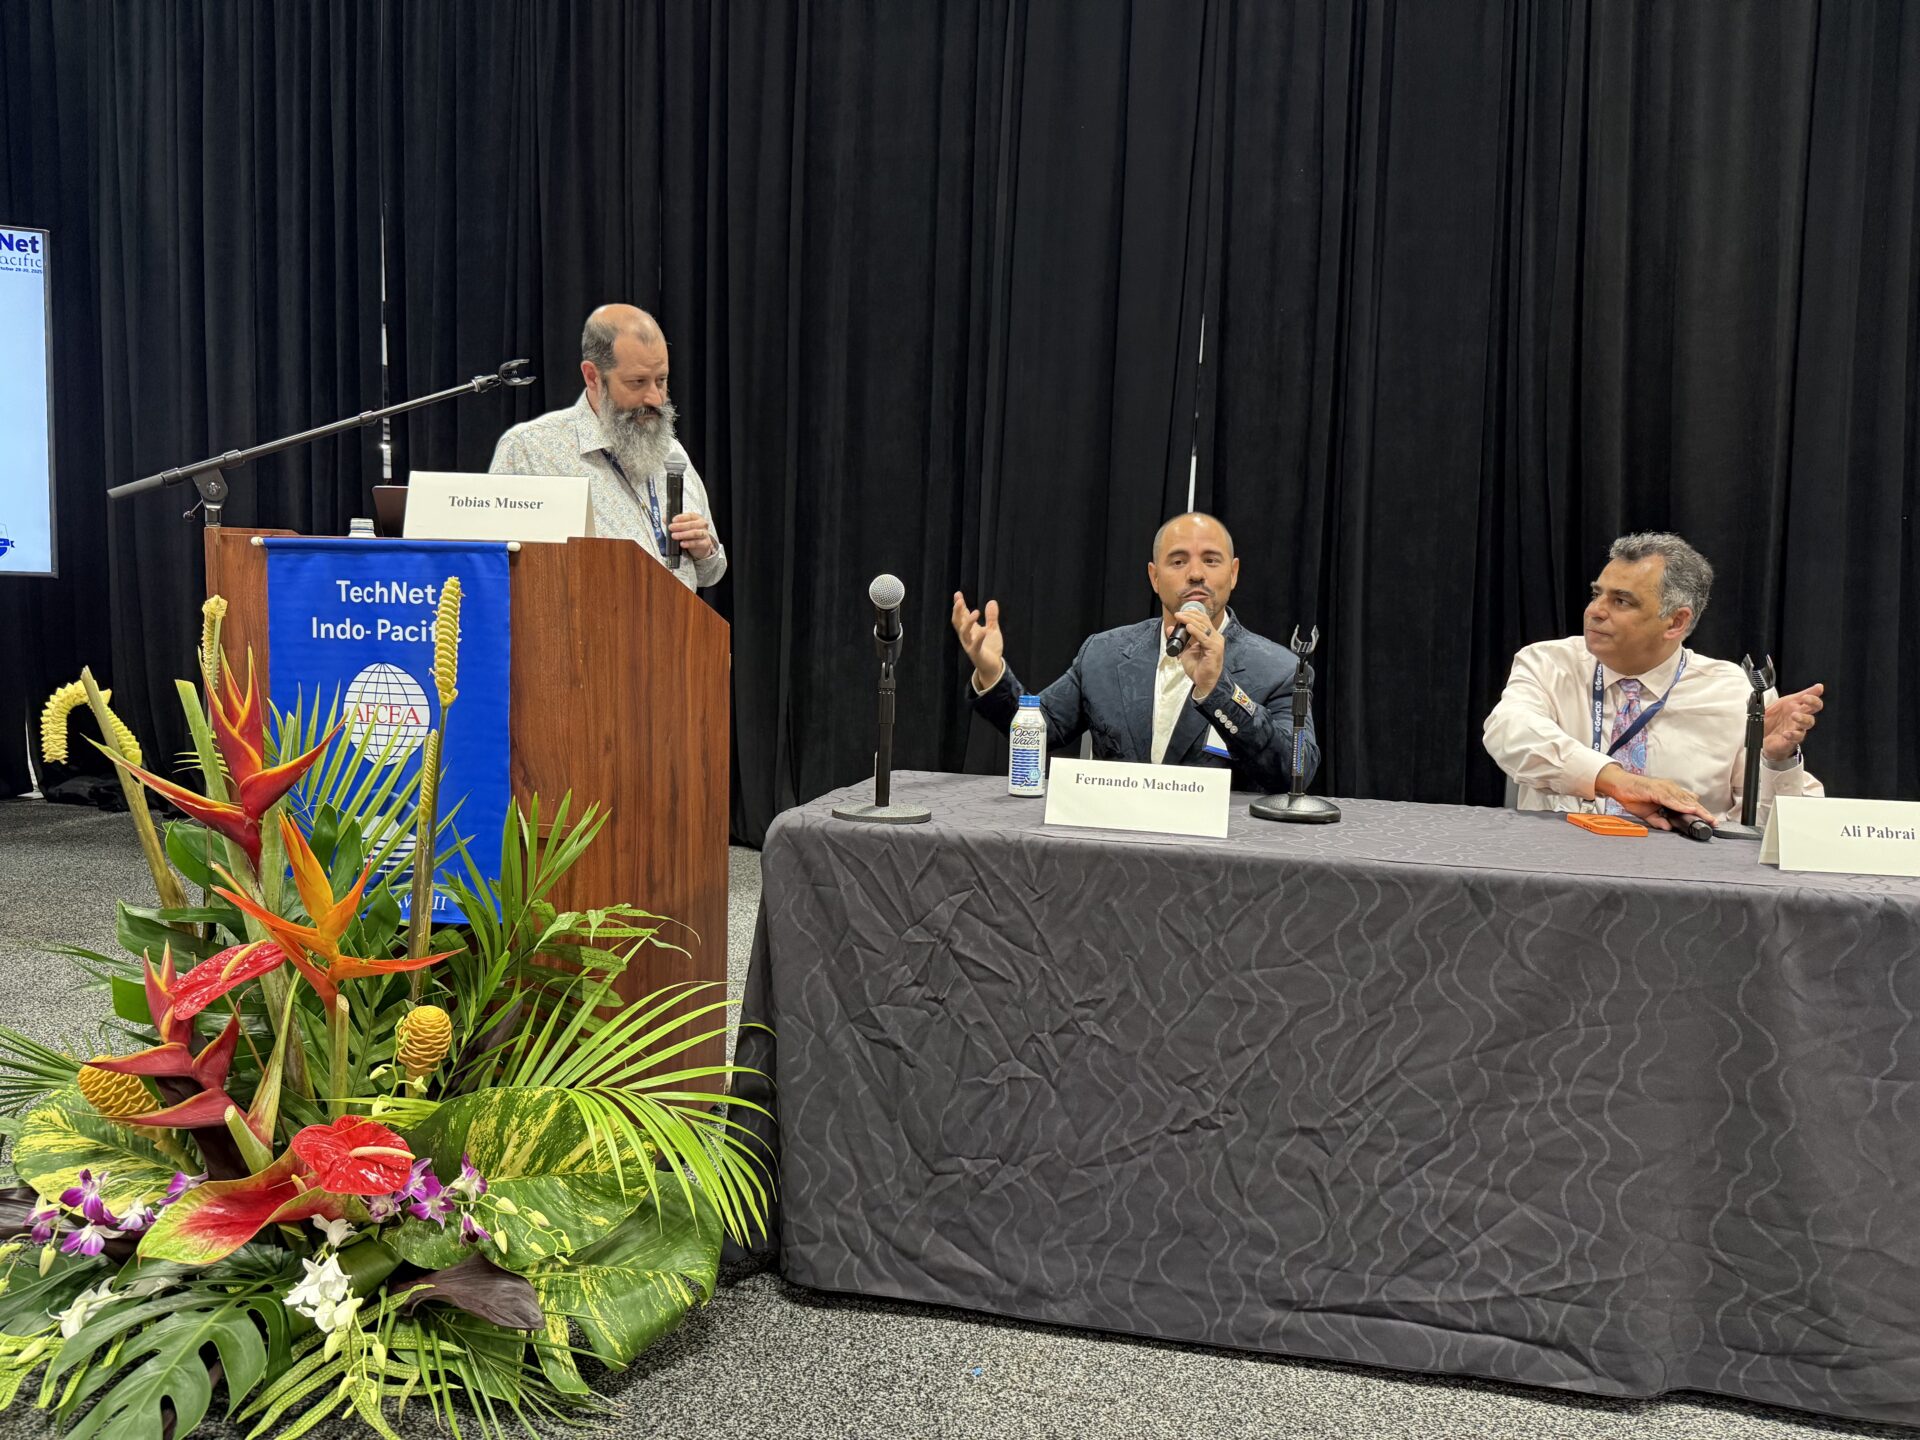
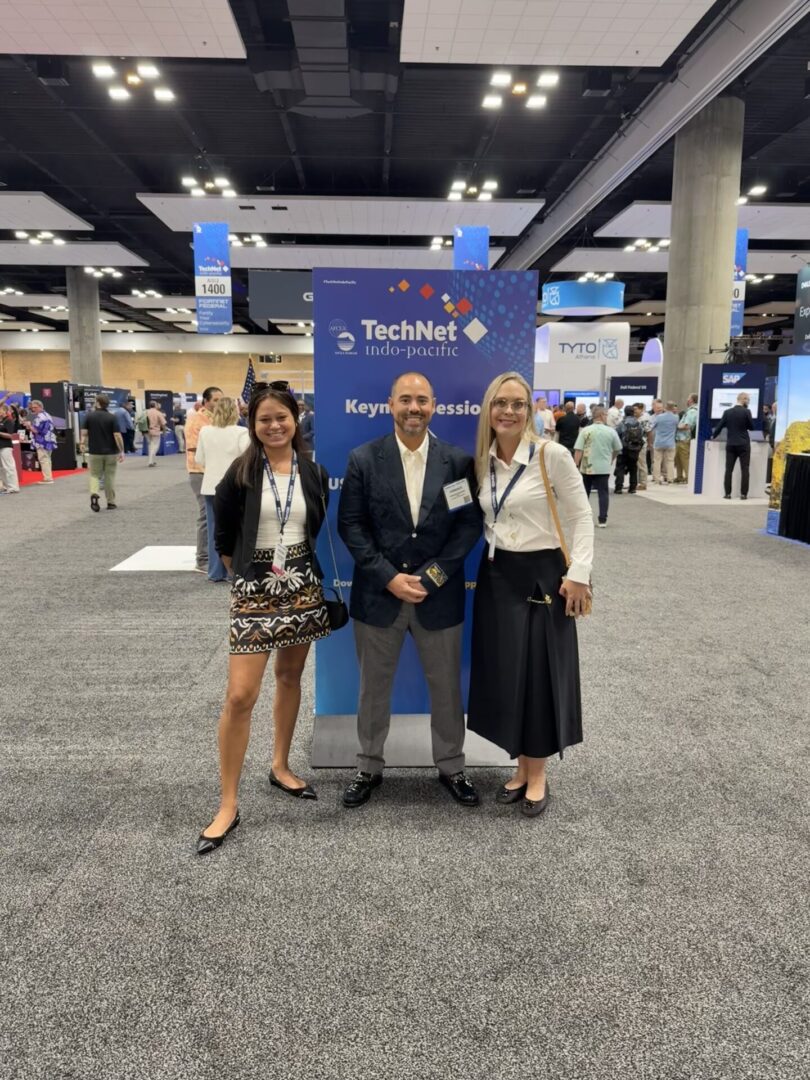
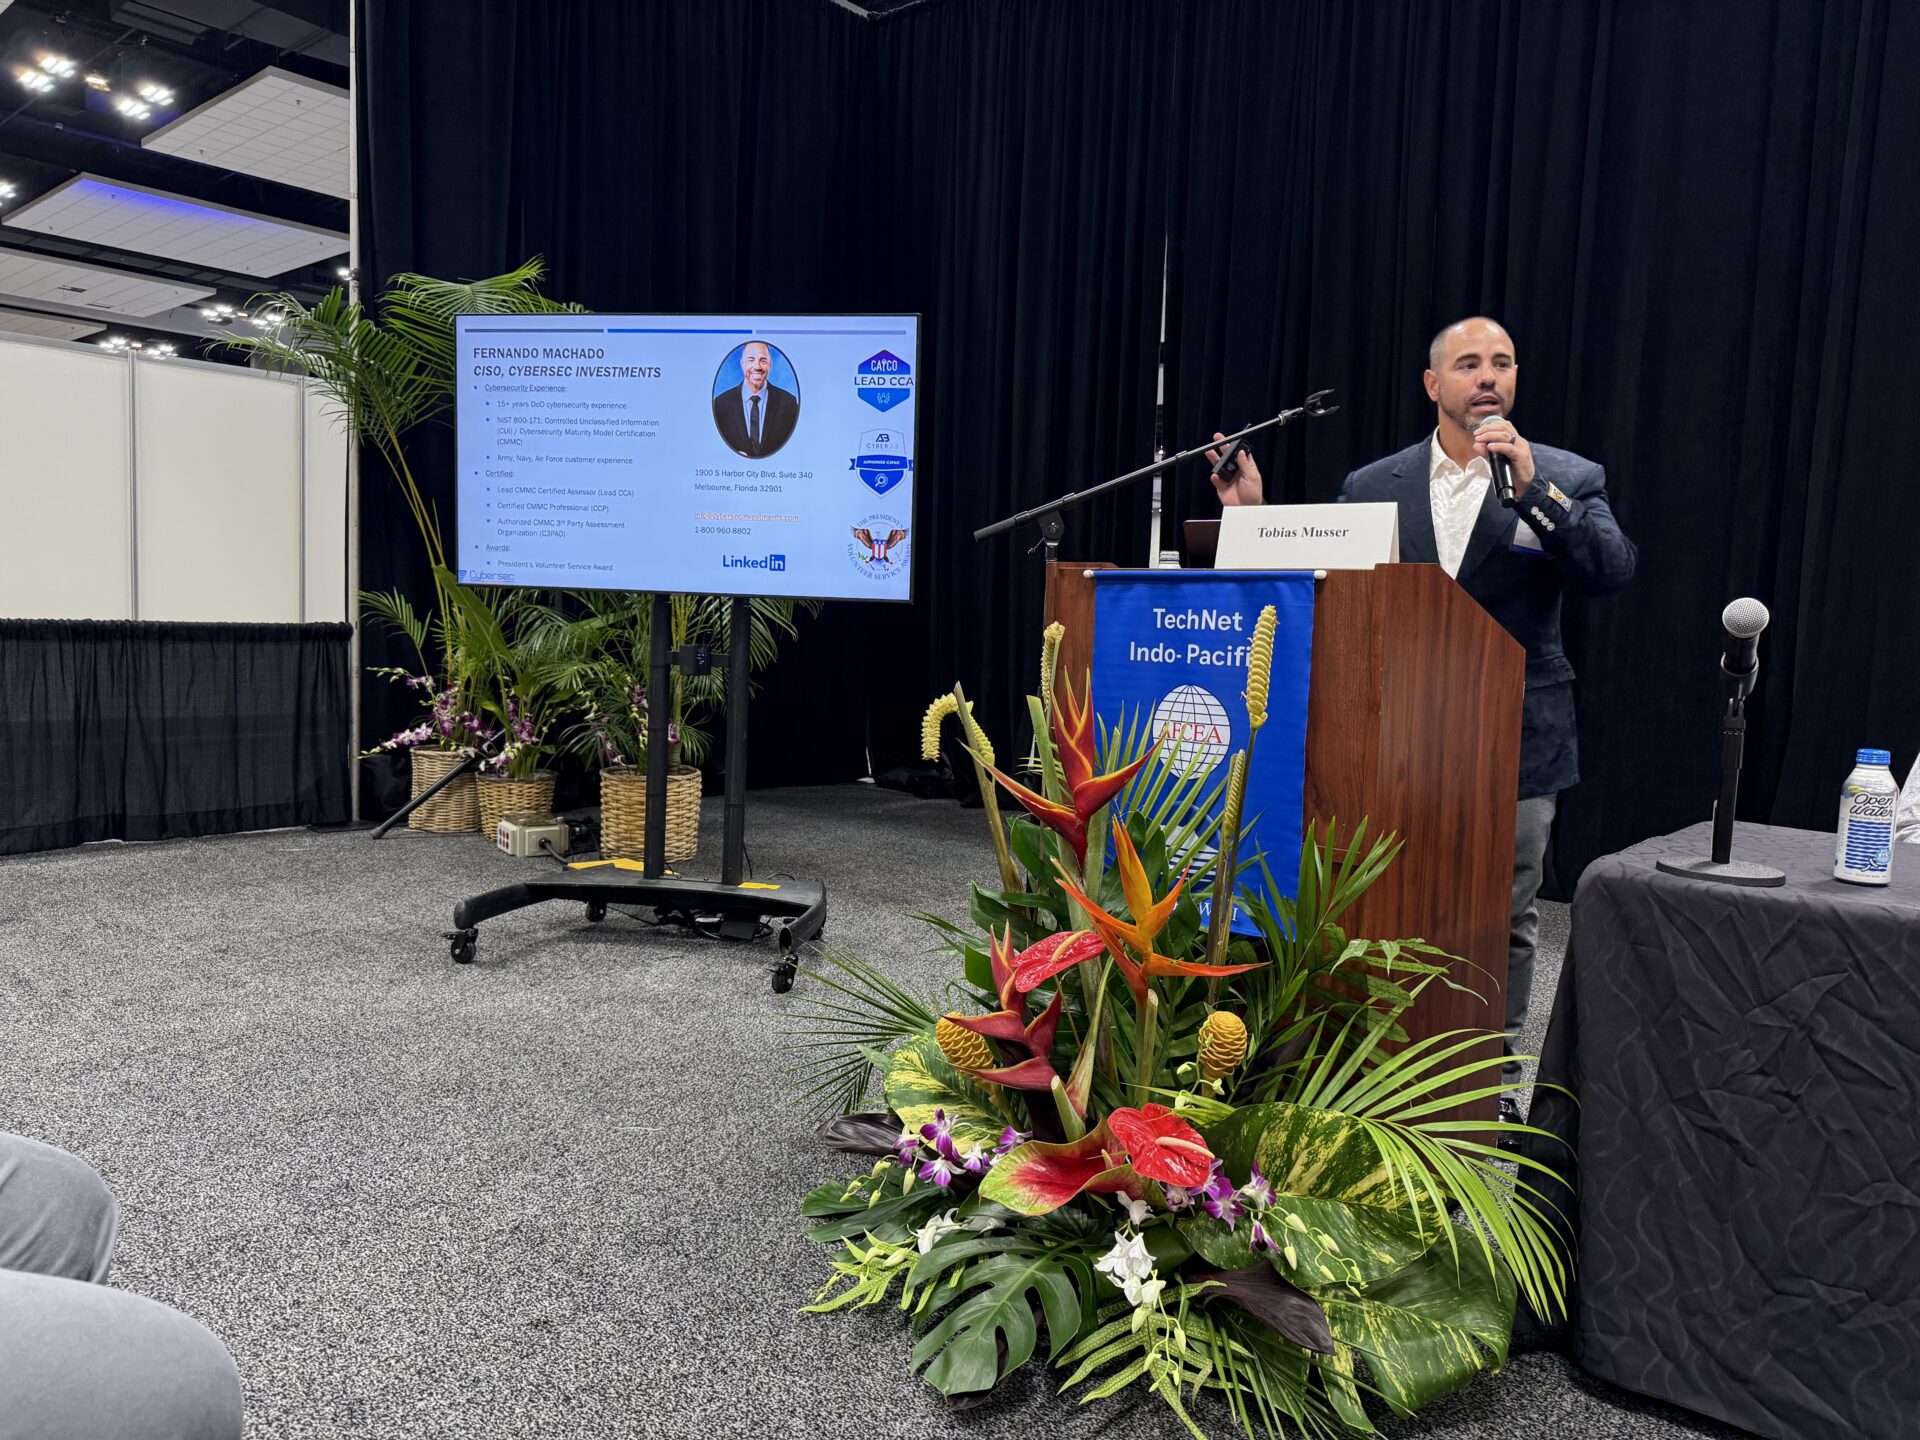
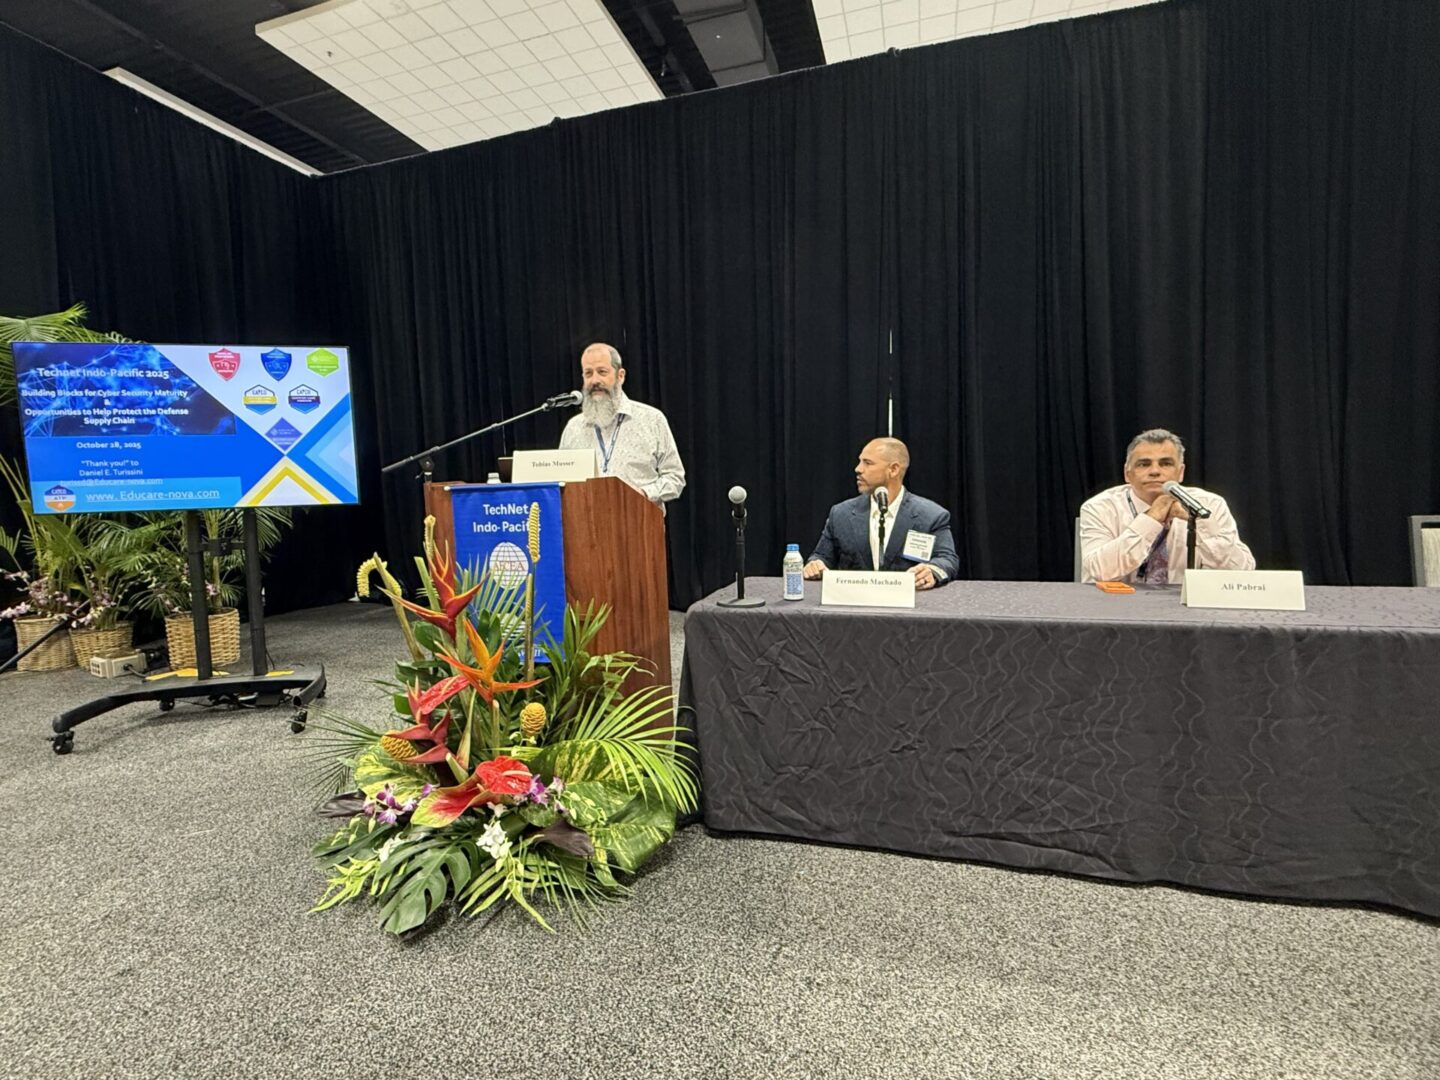
Fernando Machado Speaks at TechNet Indo-Pacific 2025 – Honolulu, HI

Managing Principal & CISO Fernando Machado, CISSP, CISM, CCA, CCP, spoke at TechNet Indo-Pacific 2025 in Honolulu, Hawaii — sharing his perspective on cybersecurity and compliance within the DIB. Nicole and Krystiana from the Cybersec Investments team attended alongside Fernando, connecting with peers dedicated to strengthening cybersecurity across the industry.

Three panelists speaking at conference tableThree people posing at TechNet Indo-Pacific conferenceMan speaking at podium beside presentation screenSpeaker at podium with two panelists

October 27, 2025

Industry

CMMC Compliance Requirements for RTX Suppliers

RTX required all suppliers supporting applicable DoD contracts to maintain an active CMMC certification with final DFARS clause 252.204-7021 effective November 10, 2025. Suppliers must report certification status in the DoD SPRS, maintain six years of evidence, and keep annual registrations current. Level 1 requires full implementation of 15 controls; Levels 2 & 3 protect CUI with POA&M accepted for certain requirements but must be closed within 180 days.

October 21, 2025

Event

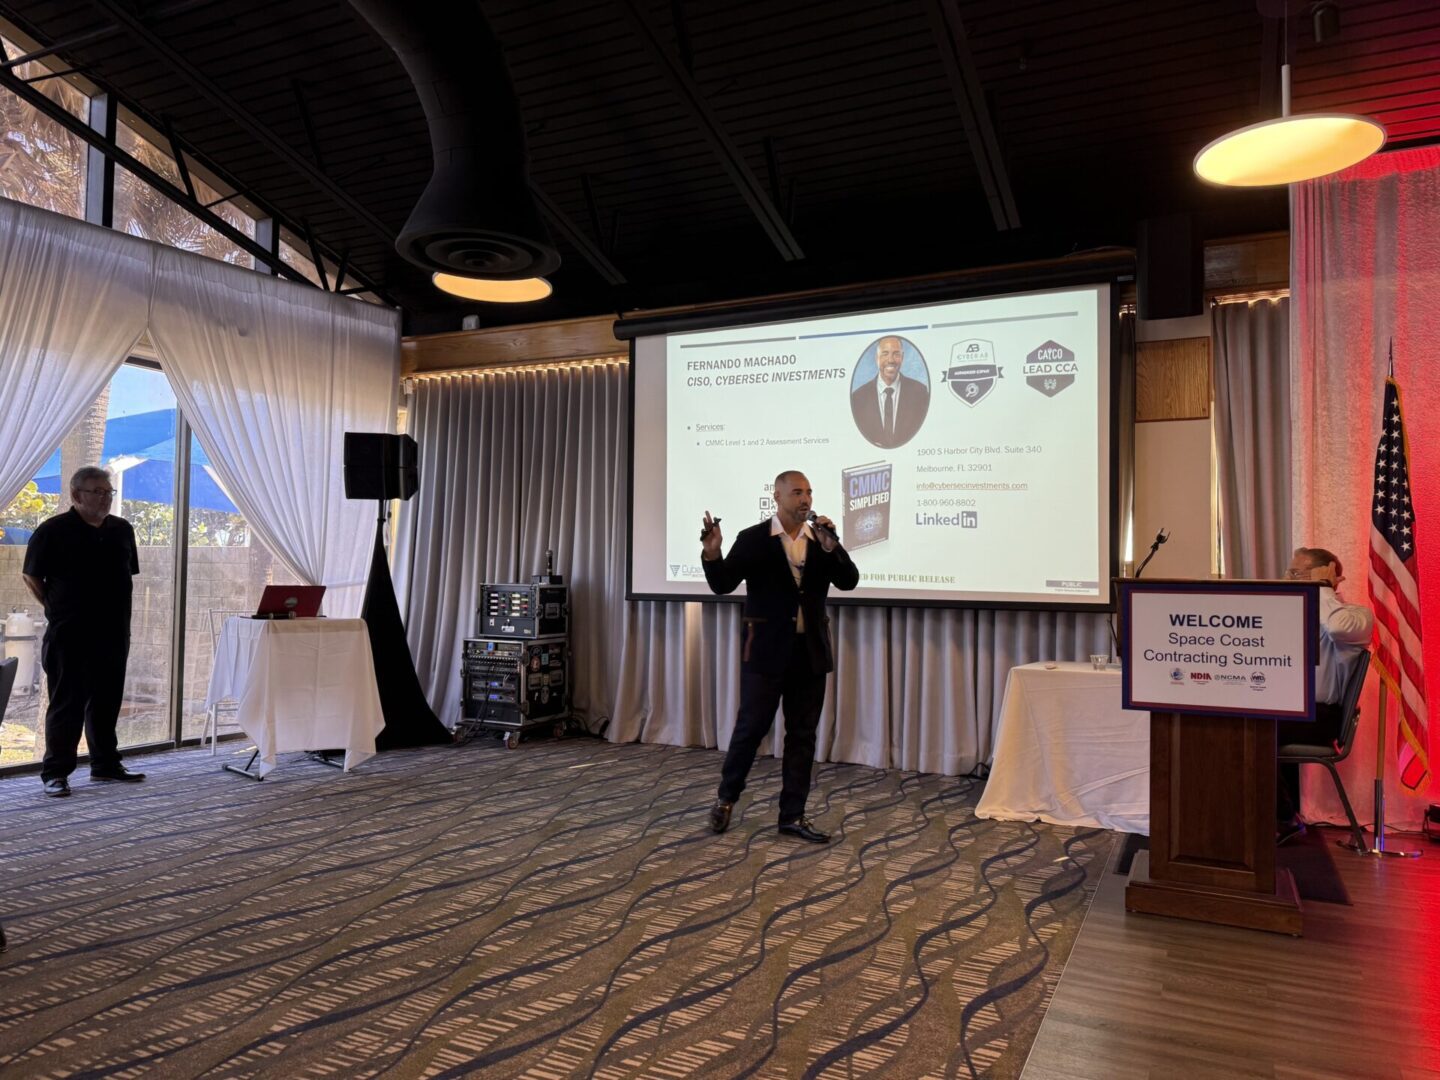
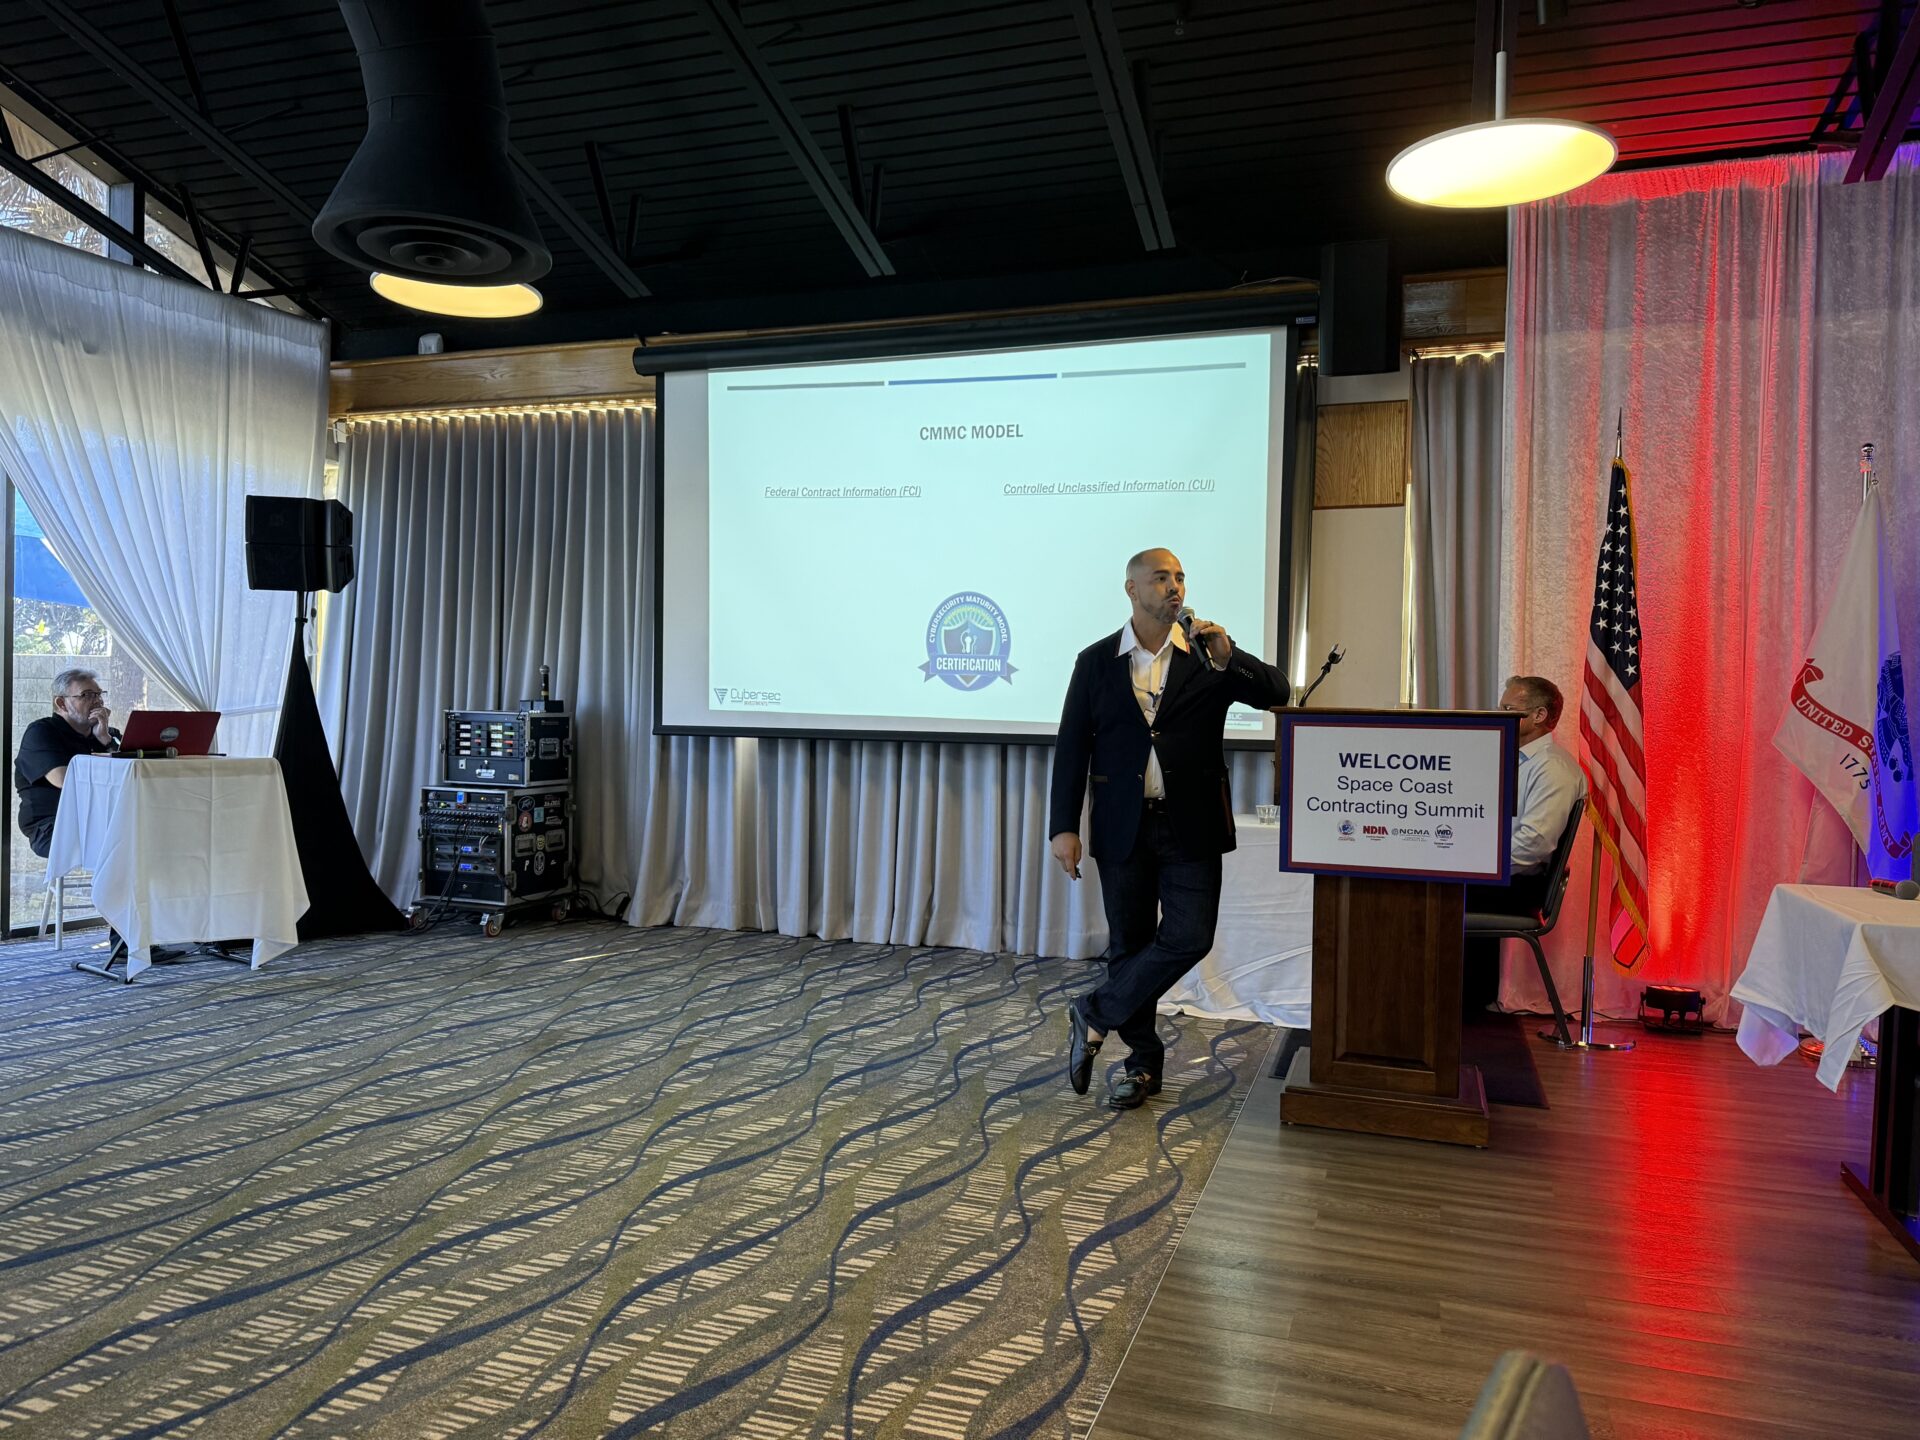
Space Coast Contracting Summit 2025 – Days 1 & 2 Recap

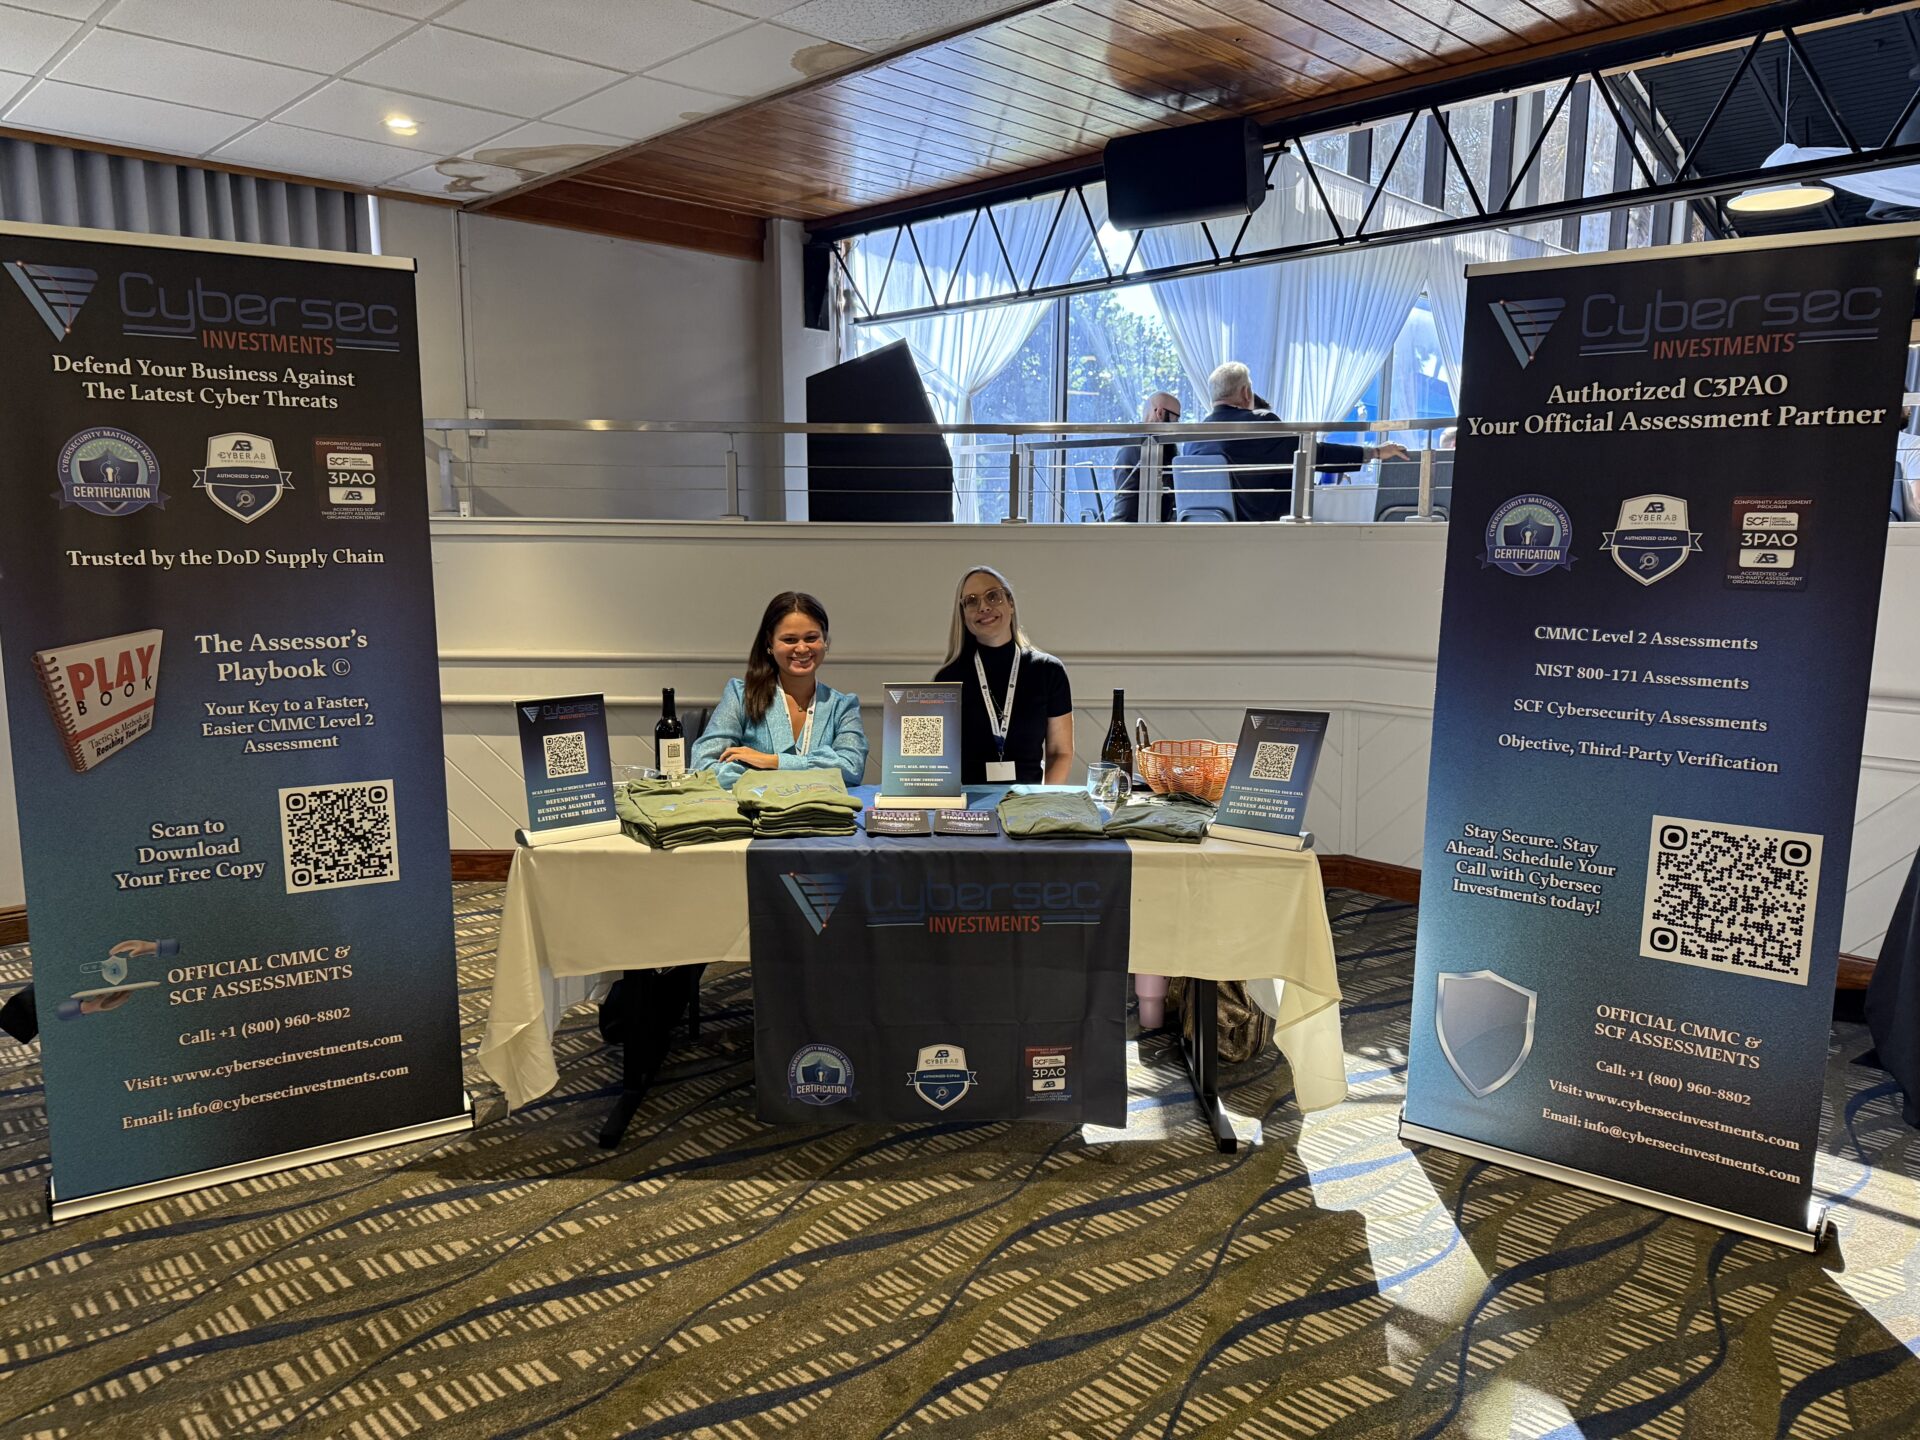
Cybersec Investments sponsored the 2025 Space Coast Contracting Summit at Patrick Space Force Base, FL. Managing Principal & CISO Fernando Machado presented “CMMC Unraveled,” and the Cybersec Investments booth served as a hub for industry conversation. Director of Client Engagement Nicole Machado and Contracts Specialist Krystiana Bouchard represented the company throughout both days.

Speaker presenting at Space Coast contracting summitSpeaker presenting at conference with projection screenTwo women at cybersecurity investments booth

October 16, 2025

Event

Fernando Machado Speaks at CS5 East 2025

Fernando Machado, CISSP, CISM, CCA, CCP, represented Cybersec Investments as a featured speaker at CS5 East 2025 in National Harbor, MD — a premier event bringing together CMMC professionals, cybersecurity leaders, and Defense Industrial Base (DIB) stakeholders to share knowledge on compliance and critical infrastructure protection.

Two people on stage with chairs.Two people on stage at a conference.Two people speaking on a conference stage.Two people speaking on stage with chairs.Three speakers on stage at a conference.Two people on stage during a presentation.

October 14, 2025

Media

ND-ISAC C3PAO Shopping Guide: A Must-Read for SMBs Seeking CMMC Compliance

Cybersec Investments shared the ND-ISAC C3PAO Shopping Guide for Small and Medium-Sized Businesses, designed to help SMBs choose a certified CMMC Third-Party Assessment Organization. The guide provides key tips, questions to ask, and best practices for a successful CMMC Level 2 assessment.

ND-ISAC logo and text on white background.

October 10, 2025

Industry

Leonardo DRS Issues Supplier Letter on CMMC 2.0 Rollout

Leonardo DRS released a notice to suppliers about upcoming CMMC 2.0 requirements appearing in select DoD contracts on November 10, 2025. Suppliers with the DFARS 252.204-7012 clause should anticipate a CMMC Level 2 (C3PAO Certified) requirement within two years. Leonardo DRS recommended suppliers close open POAM items, maintain a NIST 800-171 score of 110/110, and engage with authorized C3PAOs through the CyberAB Marketplace.

Letter about CMMC readiness for suppliers.

October 8, 2025

Event

Fernando Machado Speaks on CMMC Compliance at NDIA Tampa Bay

Managing Principal & CISO Fernando Machado participated in a high-profile panel at the NDIA Tampa Bay event discussing CMMC compliance and cybersecurity readiness for the defense industrial base. Fernando and Michael Brooks, CISSP, PMP, MBA shared actionable insights on enhancing cybersecurity maturity, implementing CMMC best practices, and preparing for evolving compliance requirements.

Two men smiling in business attire indoors.

September 29, 2025

Industry

Lockheed Martin Taking Steps to Prepare Suppliers for CMMC Level 2

Lockheed Martin moved to ensure suppliers are prepared for CMMC Level 2 with an effective date of November 9, 2025. Suppliers with Moderate or Significant risk ratings in Exostar’s CCRA should complete or update their questionnaire, close NIST 800-171 gaps, and conduct a CMMC readiness assessment. Cybersec Investments provides CMMC and SCF assessments to help suppliers evaluate readiness and build a clear compliance roadmap.

September 26, 2025

Industry

Boeing Issues Supplier Update on CMMC Compliance

Boeing released an official letter to suppliers outlining expectations for CMMC compliance. The notice emphasizes that protecting Controlled Unclassified Information (CUI) is essential and that suppliers must demonstrate CMMC readiness to remain eligible for future contracts. Cybersec Investments performs independent CMMC and SCF assessments to help organizations measure compliance posture and prepare for upcoming contract requirements.

September 24, 2025

Company

Advanced Space Achieves CMMC Level 2 Certification

Advanced Space achieved CMMC Level 2 certification following an assessment by Cybersec Investments. The certification confirms the company meets established cybersecurity standards for handling CUI and FCI under CMMC 2.0 Level 2 and DFAR 252.204-7021.

September 22, 2025

Company

Cybersec Investments Surpasses 50 CMMC Assessments!

Cybersec Investments officially completed over 50 CMMC assessments — a milestone reflecting the trust clients place in the team and dedication to guiding organizations through their CMMC readiness journey. Looking ahead: the team remains committed to delivering top-quality CMMC and SCF assessments, helping organizations stay ahead of requirements and confidently demonstrate readiness.

September 10, 2025

Industry

CMMC Final Rule Published – Effective November 10, 2025

The DoD officially published the final DFARS rule integrating CMMC into federal contracts. Key details: published September 10, 2025; effective November 10, 2025; phased rollout across contracts; affects all contractors handling FCI or CUI. Organizations should conduct a readiness assessment, build a compliance roadmap, and prepare for phased implementation.

September 10, 2025

Industry

CMMC Launches: What Businesses Need to Know

The Department of Defense officially rolled out the CMMC program with the DFARS rule published in the Federal Register. Phase 1 starts November 10, 2025. Project Spectrum provides free resources — training, self-assessments, and guidance from cybersecurity experts — to help small and mid-sized defense supply chain companies prepare.

July 23, 2025

Event

Fernando Machado Speaks at 2025 National HUBZone Conference

Managing Principal & CISO Fernando Machado spoke at the 2025 National HUBZone Conference, hosted by the HUBZone Contractors National Council. Fernando joined the panel “The CMMC HUBZone: The Small Business Guide to Navigating Compliance.” Team members Clay Mathews and Krystiana Bouchard also attended, representing Cybersec Investments among professionals dedicated to strengthening compliance in the federal space.

Three people at HUBZone event display.

July 22, 2025

Industry

48 CFR CMMC Rule Sent to Office of Management and Budget for Review

The 48 CFR rule, a critical regulation tied to CMMC, was officially sent to the OMB for review — signaling the final stages of rulemaking before CMMC becomes enforceable across DoD contracts. Once OMB completes review and the rule is published in the Federal Register, CMMC requirements will start appearing in new solicitations impacting contractors working with CUI.

Department of Defense cybersecurity requirements document snippet.

July 17, 2025

Company

Cybersec Investments Named Official SCF 3PAO

Cybersec Investments is now an officially certified SCF Third-Party Assessment Organization (3PAO) under the Cyber AB. This designation allows the team to conduct formal SCF and CMMC assessments, helping defense contractors meet compliance with clarity, credibility, and confidence.

3pao badge Conformity Assessment Program

June 26, 2025

Company

Cybersec Investments Passes DIBCAC Assessment

Cybersec Investments officially passed their Defense Industrial Base Cybersecurity Assessment Center (DIBCAC) assessment — an important step in continued growth as a trusted C3PAO. The team remains focused on delivering high-quality support to the defense industrial base.

June 10, 2025

Company

Cybersec Investments Welcomes Five New Team Members

Cybersec Investments is excited to welcome five new professionals to the growing team: Ryan Gonzalez (CMMC Certified Assessor), Sawyer Jones (CMMC Certified Assessor), James Lancaster (CMMC Certified Assessor), Cristal Rodriguez (Client Success Specialist), and Dan Labus (CMMC Certified Assessor). Each brings valuable expertise and a commitment to supporting organizations across the defense industrial base.

Team announcement poster with six staff portraits

June 6, 2025

Company

Cybersec Investments Completes 25 CMMC Assessments

In just a few short months since beginning CMMC assessments, Cybersec Investments completed 25 assessments for organizations in the defense industrial base — reflecting the team’s focus, precision, and commitment to supporting contractors through every step of the compliance process.

May 21, 2025

Event

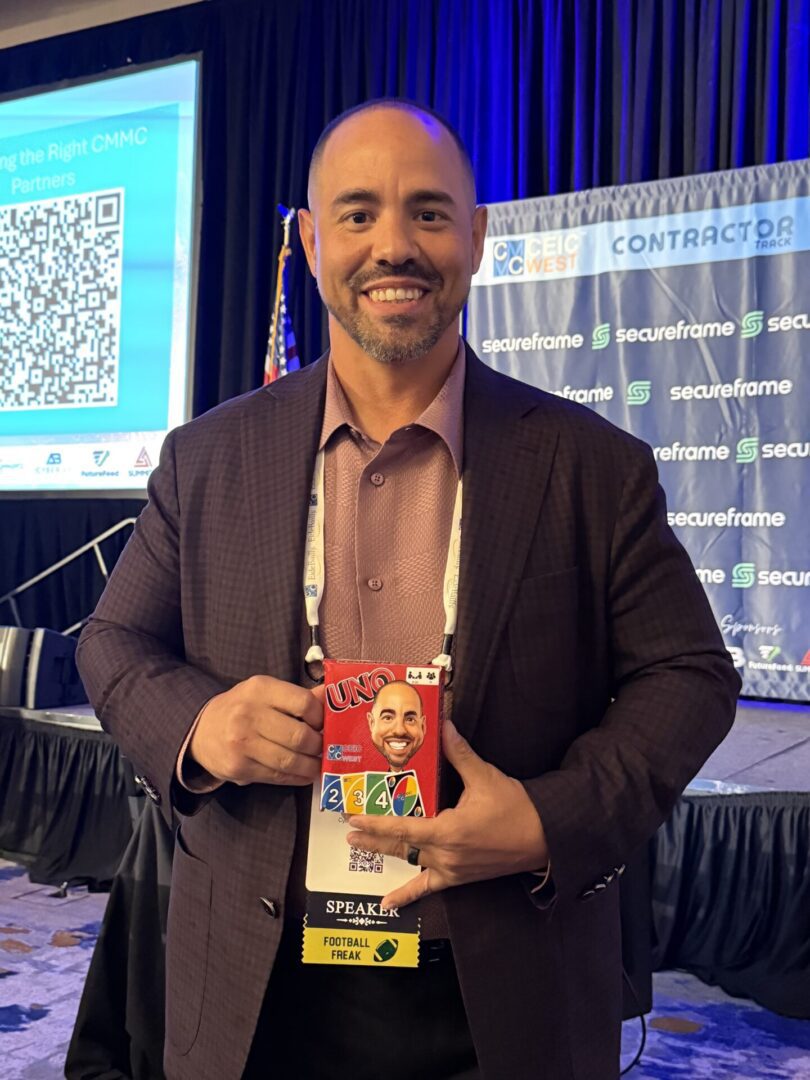
Fernando Machado Speaks at CEIC West – Las Vegas

Fernando Machado, Managing Principal & CISO, spoke at CEIC West in Las Vegas, where industry leaders and government professionals gathered to discuss CMMC, compliance, and the future of defense cybersecurity.

a man with his trophy smiling

May 7, 2025

Event

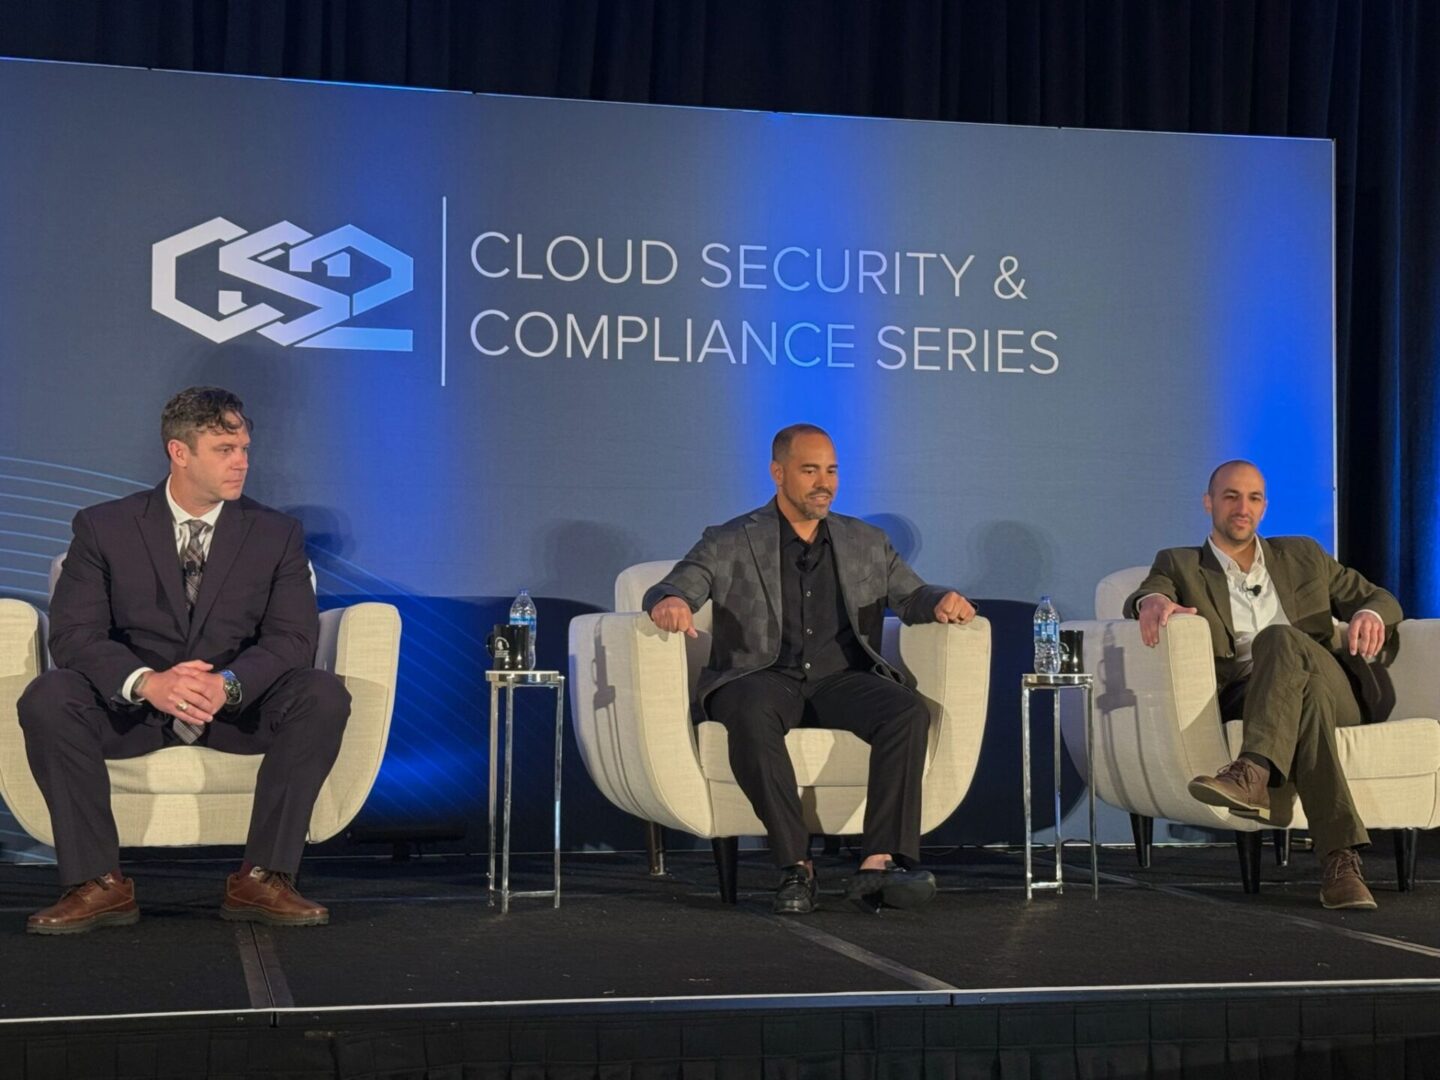
Fernando Machado Speaks at CS2 Reston

Managing Principal & CISO Fernando Machado spoke at CS2 Reston — a key event focused on cybersecurity and compliance in the defense industrial base, hosted by Summit 7. The event brought together leaders across the industry to share CMMC updates and best practices for navigating DoD requirements.

three men are sitting on the chairs for an event

May 5, 2025

Event

Fernando Machado Speaks at CMMC Day

Managing Principal & CISO Fernando Machado joined leaders across the industry for a full day of discussions centered on compliance, implementation, and what’s next for the CMMC ecosystem.

CMMC day POST ON NEWS

April 29, 2025

Event

Fernando Machado Speaks at RSA Conference – San Francisco

Managing Principal & CISO Fernando Machado had the honor of speaking at the RSA Conference in San Francisco. His session, “Turning Breaches into Best Practices,” focused on real-world lessons from security incidents and how to use them to strengthen future cyber resilience.

RSAC Event POST ON NEWS

February 27, 2025

Event

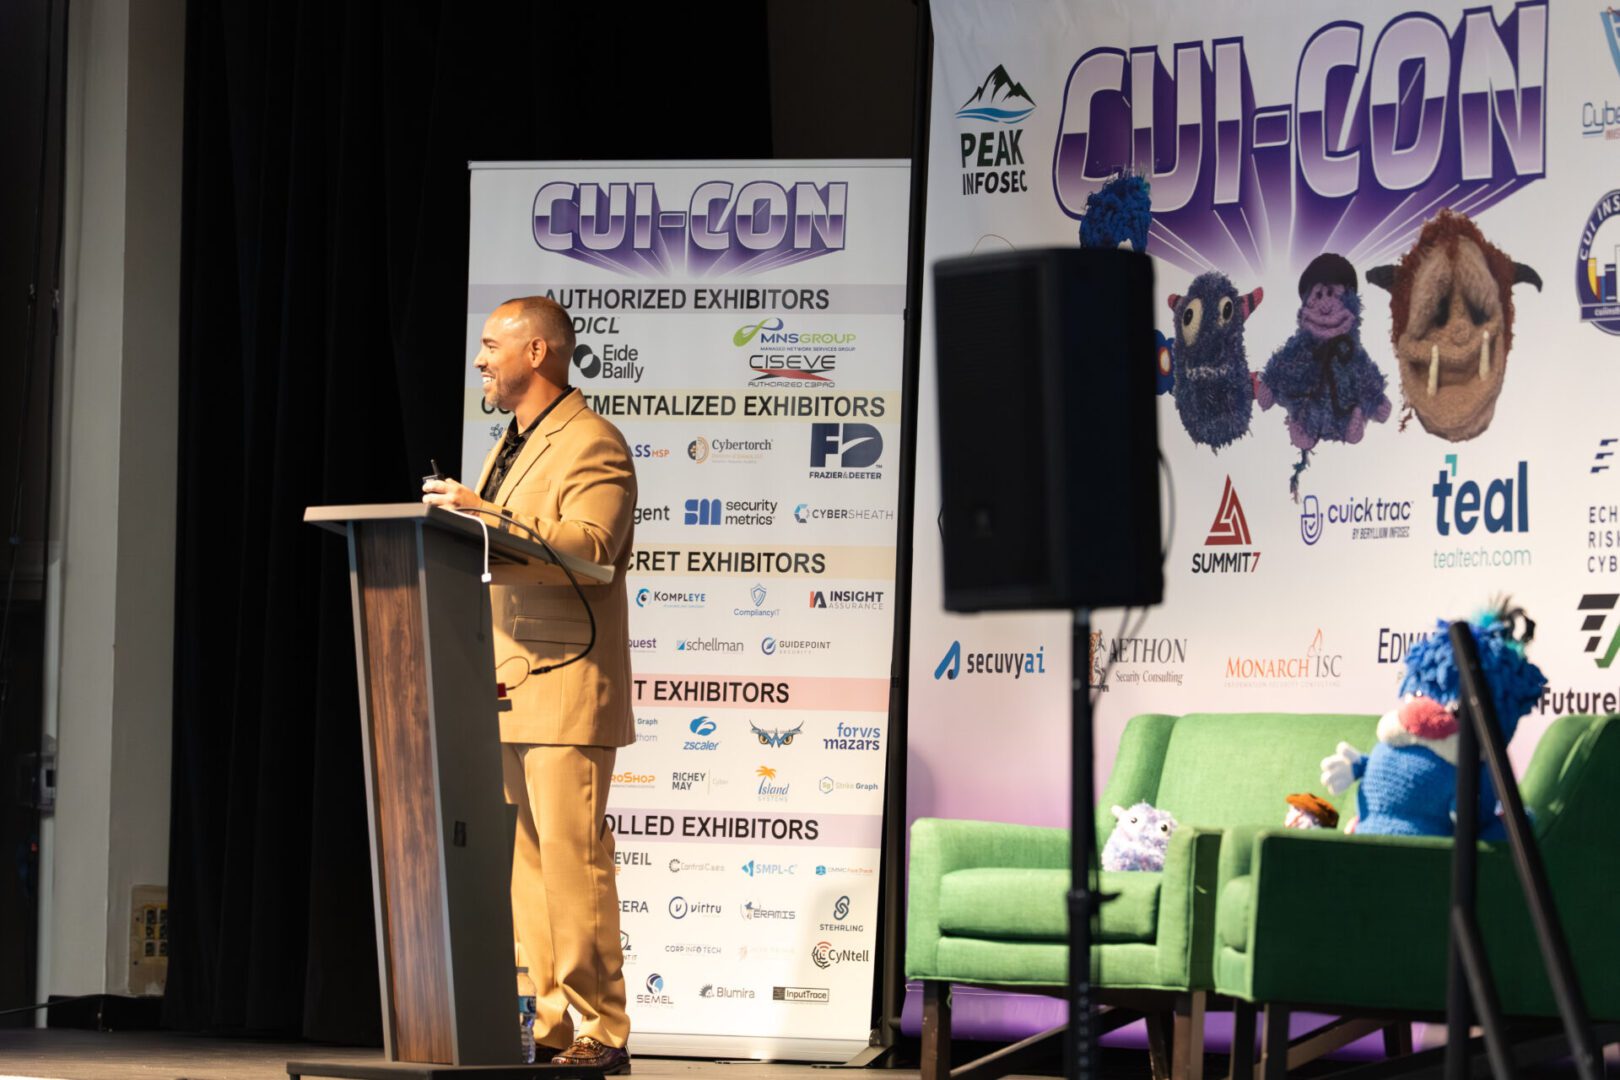
Fernando Machado Speaks at CUI-CON – Tampa, FL

Fernando Machado spoke at CUI-CON in Tampa, FL on February 27–28, 2025, held at the Tampa Airport Marriott. He joined other industry leaders to support DoD contractors in implementing NIST SP 800-171 and preparing for CMMC assessments.

two men are giving a presentation on stage
2024

December 16, 2024

Industry

CMMC 2.0 Completes 60-Day Congressional Review — Program Now in Effect

CMMC 2.0 completed its 60-day Congressional Review period without any changes. Rulemaking is now complete and the new program is in effect. Companies should begin working towards their CMMC certifications and C3PAOs can begin assessments in accordance with the guidance in the rule.

August 7, 2024

Industry

OIRA Concludes Review of 48 CFR Proposed CMMC Rule

The Office of Information and Regulatory Affairs (OIRA) concluded its review of the 48 CFR proposed CMMC rule — the contract clause that will be added to a defense contractor’s contractual agreement (DFARS 252.204-7021). The next step is publication in the Federal Register and a public comment period.

June 27, 2024

Industry

Update on the CMMC Program

The Department of Defense submitted the CMMC Program rule to OIRA for final review and publication. OIRA has 90–120 days to review, putting the publication date between late September through late October. Once published in the Federal Register, the rule will be effective 60 days later, making the CMMC Program official.

A group of people posing for a picture.

June 25, 2024

Event

AFCEA TechNet Cyber

Fernando Machado was invited to Baltimore to join a panel of cyber professionals on the topic of “Building Blocks for Cyber Security Maturity and Opportunities to Help Protect the USA Supply Chain.” Thank you to AFCEA for the invitation — the event was a great success!

A group sitting at chairs in a board room

June 7, 2024

Industry

Update on the CMMC Program

DoD plans to start the CMMC rollout in Q1 2025. Organizations should begin preparing now to ensure readiness when the rule takes effect.

May 14, 2024

Industry

NIST 800-171 Rev 3 Released

The long awaited NIST SP 800-171 revision 3 and NIST SP 800-171A revision 3 have been published — establishing updated cybersecurity requirements for protecting CUI in nonfederal systems and organizations.

May 2, 2024

Industry

Department of Defense Class Deviation Released

The DoD released a class deviation on DFARS 252.204-7012 to require contractors to comply with NIST SP 800-171 rev. 2, which will remain in effect until rescinded instead of the NIST SP 800-171 “in effect at the time the solicitation is issued or as authorized by the Contracting Officer.”

February 22, 2024

Event

CUI-CON Orlando

Thank you to everyone who made CUI-CON a memorable event. Photos from the event have been posted and can be viewed via the link shared at the event.

February 5, 2024

Media

New Article from Brevard Business News

Brevard Business News featured Cybersec Investments in their February 5 issue, titled “Cybersec Investments helps DOD contractors gear up for CMMC compliance; founder Machado to put on conference in Orlando featuring industry experts.”

BBN Article
2023

December 22, 2023

Industry

CMMC Rule Published to the Federal Register

The Cybersecurity Maturity Model Certification (CMMC) Program rule has been published to the Federal Register. This marks an important milestone in the formalization of CMMC requirements for defense contractors.

December 6, 2023

Company

A Small Subcontractor Passes a JSVA Assessment with a Perfect 110

Koren Wise featured an article titled “A Very Small Subcontractor Passed the JSVA This Week with Flying Colors” about Jaco Aerospace passing their Joint Surveillance Voluntary Assessment (JSVA) with a perfect score of 110 — conducted by Cybersec Investments.

Jaco JSVA Passing poster

November 8, 2023

Event

2nd Annual CMMC Ecosystem Summit

Cybersec Investments’ Fernando Machado was asked to be a panelist on the topic of “Understanding CUI, FCI, and ITAR” with Matt Titcombe.

A large group of people sitting at tables and some people speakingA big hall with presentations going on and a lot of people sitting at tables.

November 7, 2023

Media

Regulatory Phishing Podcast: “The When, Where, Why and How of CMMC with Fernando Machado”

Fernando Machado joined Government Contracts and Cybersecurity attorney Eric Crusius of Holland & Knight for an episode of the Regulatory Phishing Podcast focused on CMMC. Mr. Crusius and Mr. Machado discuss the current state of CMMC, how companies can come to terms with the certification program, and strategies for compliance. They also walk through Mr. Machado’s book, CMMC Simplified.

November 3, 2023

Company

DTS Passes Their JSVA!

Congratulations to DTS for passing their Joint Surveillance Voluntary Assessment (JSVA)! Thank you for your vote of confidence in choosing Cybersec Investments as your Authorized CMMC 3rd Party Assessment Organization (C3PAO).

The poster of congratulations on passing Jsva

October 12, 2023

Event

GovCon Giants Government Contracting Summit 2023

Fernando Machado was part of the panel “Cybersecurity Compliance for Government Contracts.” Thank you to GovCon Giants for inviting us to be part of their inaugural event!

A man standing in front of a pictureThree people posing for a picture at an event.

September 1, 2023

Company

IVA’AL Solutions Passes Their JSVA with a Perfect 110!

Congratulations to IVA’AL Solutions, LLC for passing their Joint Surveillance Voluntary Assessment (JSVA) with a perfect 110! Thank you for choosing Cybersec Investments as your Authorized CMMC 3rd Party Assessment Organization (C3PAO). Fantastic job by all involved in making this assessment go so smoothly!

A person holding up a shield with a gold ribbon around it.

January 18, 2023

Event

CIC 2023 | San Diego

Thanks to FutureFeed and CMMC Information Institute for a fantastic event in San Diego! Cybersec Investments was privileged to be invited and to speak at the event.

A man and woman posing for the camera.
2022

August 17, 2022

Event

2022 Federal Contracting Conference

US Congressman Bill Posey put on a fantastic event at the Florida Solar Energy Center. Thank you to his office for asking Fernando Machado to speak at the event.

A group of people sitting at tables in front of microphones.

August 5, 2022

Company

Cybersec Investments is Now an Authorized C3PAO

Cybersec Investments received our Authorization letter from the Cyber AB and is now authorized to perform voluntary CMMC Assessments. Contact us for additional information.

April 22, 2022

Media

Parabilis — So, What’s the Deal with CMMC?

Teresa Moon of Parabilis featured Cybersec Investments in her recent blog post on CMMC 2.0, discussing what defense contractors need to know about the certification program.

January 24, 2022

Company

Fernando Machado Receives President’s Volunteer Service Award

Fernando Machado was recognized by the CMMC Accreditation Body for being a former member of their Standards Management Committee Industry Working Group. This group had a combined 17,432 volunteer hours working on CMMC assessment criteria, scoping, and more.

January 18, 2022

Event

CS2 — San Diego

Fernando Machado’s presentation on “Marking CUI in Your I.T. Environment” from CS2 San Diego is now available to watch online.

2021

November 19, 2021

Media

Spilling the Tea on GovCon: Understanding CMMC 2.0 with Fernando Machado

Presented by Parabilis — Fernando Machado, CEO of Cybersec Investments, brings the community up to speed on CMMC and what version 2.0 means for contractors of all sizes for the immediate future and going forward. A must-see event covering the significant changes from the original compliance proposition.

September 22, 2021

Media

Spilling the Tea on GovCon: Self Assessment vs Third Party Certification

Presented by Parabilis — Cybersecurity is in every conversation concerning federal contracting. With changing standards, government contractors must be mindful of deadlines and benchmarks. Fernando Machado hashes out what we know to be true, fixed deadlines, and establishing a plan for certification.

Ready to Start Your CMMC Journey?

Cybersec Investments is an Accredited C3PAO performing CMMC Level 2 and SCF assessments. Let's talk about your path to certification.